ISO 27001
Achieve excellence and compliance with ISO 27001 using a complete ISO 27001 software. Manage ISO 27001 requirements, perform ISO 27001 risk assessment, and optimize incident response in a single cloud-based platform.
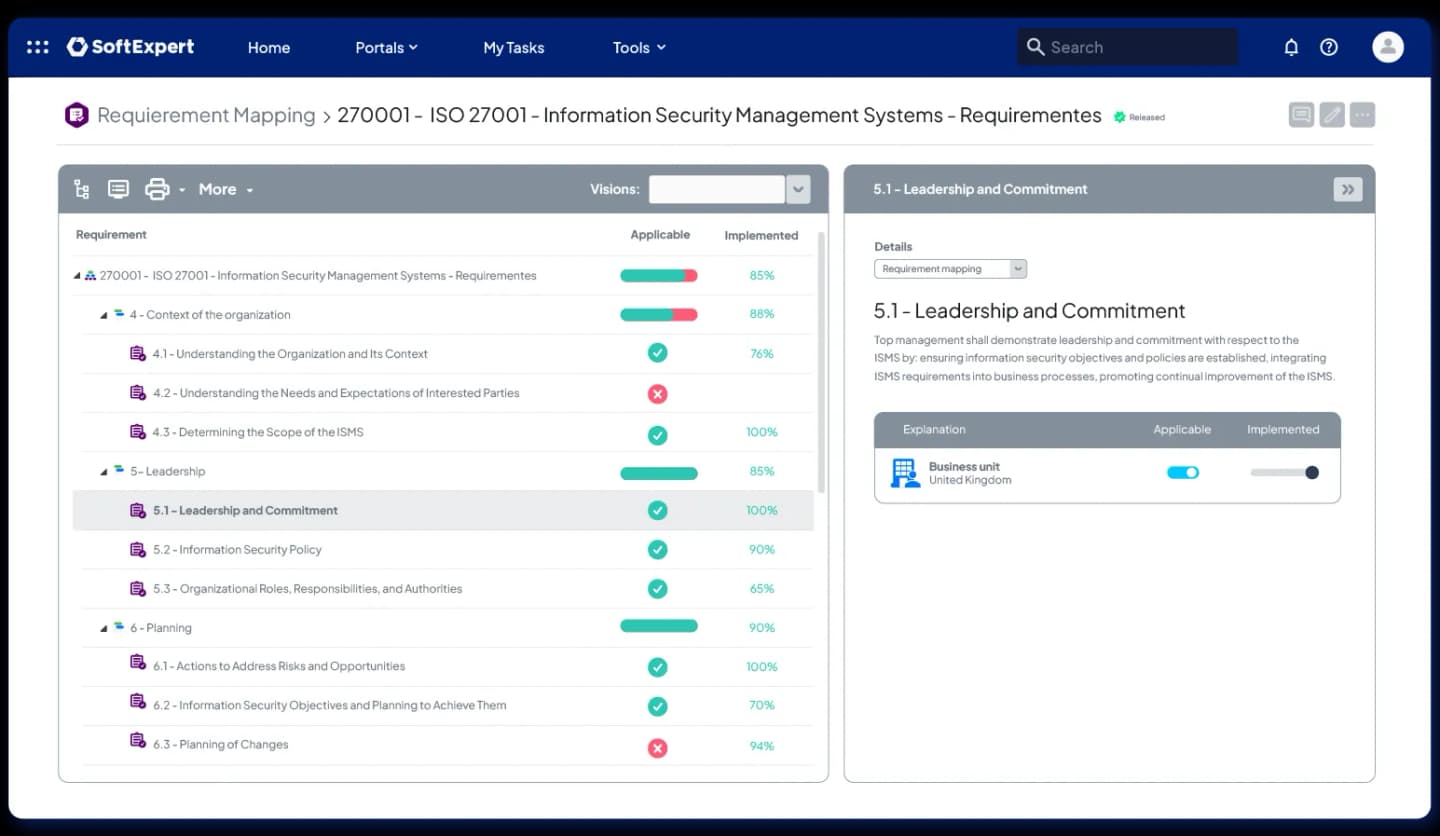

Accelerate your ISO 27001 certification journey
Centralize ISO 27001 requirements and ISO 27001 controls, simplify ISO 27001 audit, and reduce vulnerabilities with ISO 27001 compliance software.
Implement workflows for incident detection and response, strengthening data protection throughout the ISO 27001 certification process.
Improve decision-making with ISO 27001 risk assessment aligned with ISO 27001 certification.
Discover how SoftExpert helps companies achieve compliance with ISO 27001
Anticipate and mitigate risks with agility
Accelerate compliance with the ISO 27001 requirements:
6.1 - Actions to address risks and opportunities
8.2 - Information security risk assessment
8.3 - Information security risk treatment
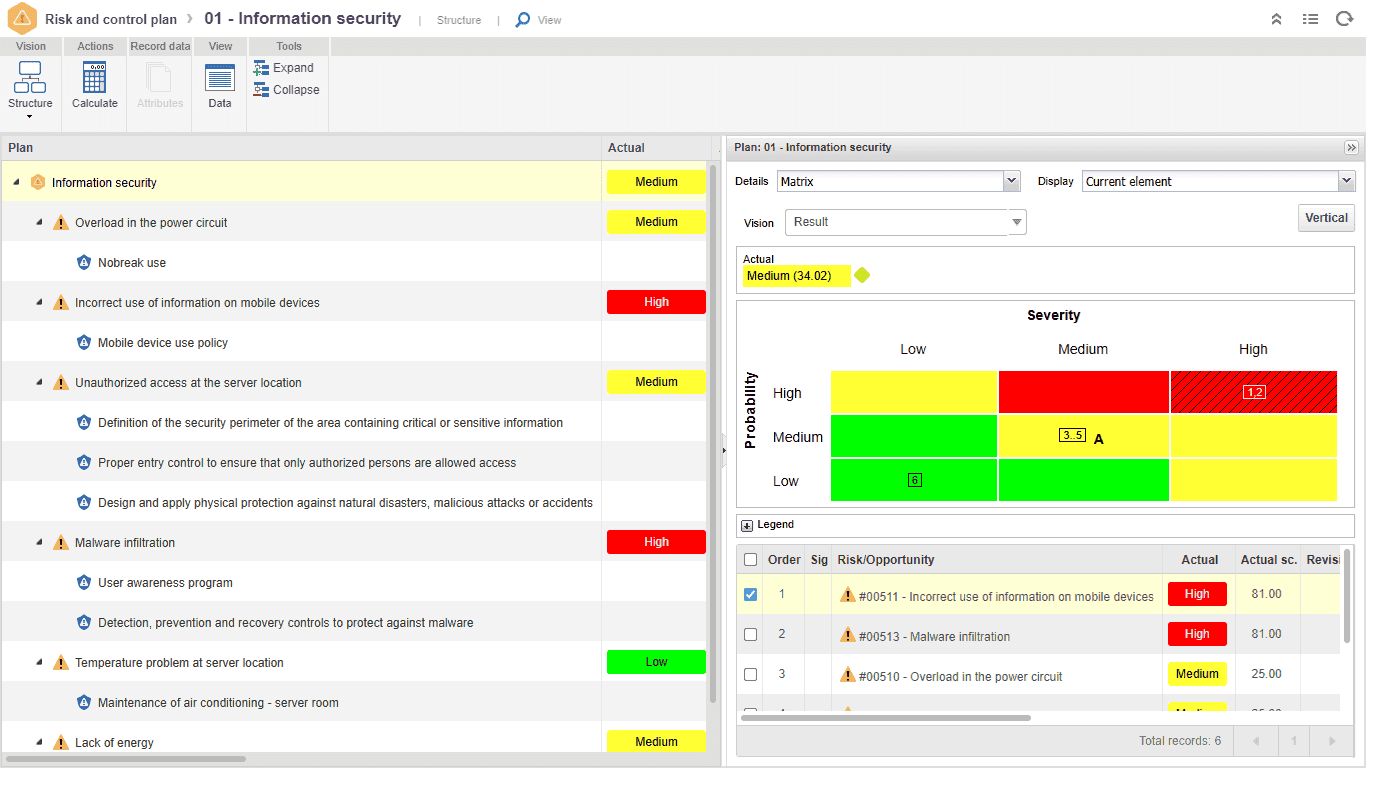
- Identification and management of information security risks
- Centralization and protection of risk information
- Prioritization of preventive actions based on contexts and impacts
- Monitoring of risk and security evolution through intuitive dashboards
Take a tour of the software. Click here →
A decision capable of changing the game
Large companies in the market have already recognized our global potential and have become our allies.
Your company could be next.
Glossary
Secure, compliant, and ready to integrate with your ecosystem
Built to connect with your existing stack while keeping governance, traceability, and control at the center.
Frequently Asked Questions
ISO 27001 is an internationally recognized standard that defines the requirements for implementing an Information Security Management System (ISMS). Its main purpose is to help organizations protect sensitive information and manage security risks in a structured and continuous way.
By adopting ISO 27001, organizations can:
- Protect critical data against breaches, unauthorized access, and cyber threats
- Establish structured ISO 27001 controls aligned with business risks
- Implement a continuous ISO 27001 risk management framework
- Ensure compliance with legal, regulatory, and contractual requirements
- Support internal and external ISO 27001 audit processes
- Strengthen governance, trust, and market credibility
With the support of ISO 27001 software, these processes become more automated, traceable, and scalable.
The ISO 27001 certification process follows a structured approach to ensure that an organization’s ISMS meets all ISO 27001 requirements.
This process typically includes:
- Defining the ISMS scope, including assets, systems, and business processes
- Conducting an ISO 27001 gap analysis to identify compliance gaps
- Implementing required ISO 27001 controls and security policies
- Performing a comprehensive ISO 27001 risk assessment
- Preparing and managing required ISO 27001 documentation
- Executing internal audits using an ISO 27001 audit checklist
- Undergoing an external certification audit conducted by an accredited body
Using an ISO 27001 compliance software significantly reduces manual effort and accelerates certification timelines.
ISO 27001 requirements define the essential elements needed to establish, implement, maintain, and continuously improve an ISMS. These requirements include:
- Defining security policies, scope, and governance structure
- Performing continuous ISO 27001 risk assessment and treatment
- Implementing and maintaining ISO 27001 controls
- Managing documentation and evidence (ISO 27001 documentation)
- Assigning roles and responsibilities for information security
- Monitoring performance through audits and reviews
- Driving continuous improvement of the ISMS
Together, these elements ensure a consistent and risk-based approach to information security.
ISO 27001 risk assessment is a core component of the ISMS and ensures that risks are identified, evaluated, and treated effectively. The process involves:
- Identifying information assets and their business value
- Detecting potential threats and vulnerabilities
- Assessing risk impact and likelihood
- Prioritizing risks based on severity
- Selecting appropriate ISO 27001 controls to mitigate risks
- Continuously monitoring and reviewing risks through ISO 27001 risk management
With ISO 27001 software, organizations can automate this process and gain real-time visibility through dashboards and analytics.
ISO 27001 software is a specialized solution designed to support the implementation, management, and maintenance of an ISMS. It helps organizations to:
- Manage and track ISO 27001 requirements and controls
- Automate audit processes and evidence collection (ISO 27001 audit)
- Perform and monitor ISO 27001 risk assessment
- Centralize policies and documentation (ISO 27001 documentation)
- Track progress throughout the ISO 27001 certification process
- Improve traceability, accountability, and efficiency
As a result, organizations can achieve compliance faster and with greater accuracy.
Implementing ISO 27001 provides both strategic and operational advantages, especially for organizations dealing with sensitive data. Key benefits include:
- Reduced security risks through structured ISO 27001 risk management
- Stronger protection of confidential and critical information
- Improved compliance with regulations and industry standards
- Increased trust from customers, partners, and stakeholders
- Better preparedness for ISO 27001 audit processes
- Continuous improvement aligned with ISO 27001 requirements
- Enhanced operational efficiency with the support of ISO 27001 software
These benefits contribute directly to business resilience and competitive advantage.
An award-winning platform recognized by customers
Trusted by users and rated across leading software review platforms for value, usability, and support.
Global Thinking with Local Service
SoftExpert's global presence, with operations on every continent, drives its growth by delivering strong, personalized service tailored to each local market.
Contact us