ISO 27001
Achieve excellence and compliance with ISO 27001 using a complete ISO 27001 software. Manage ISO 27001 requirements, perform ISO 27001 risk assessment, and optimize incident response in a single cloud-based platform.
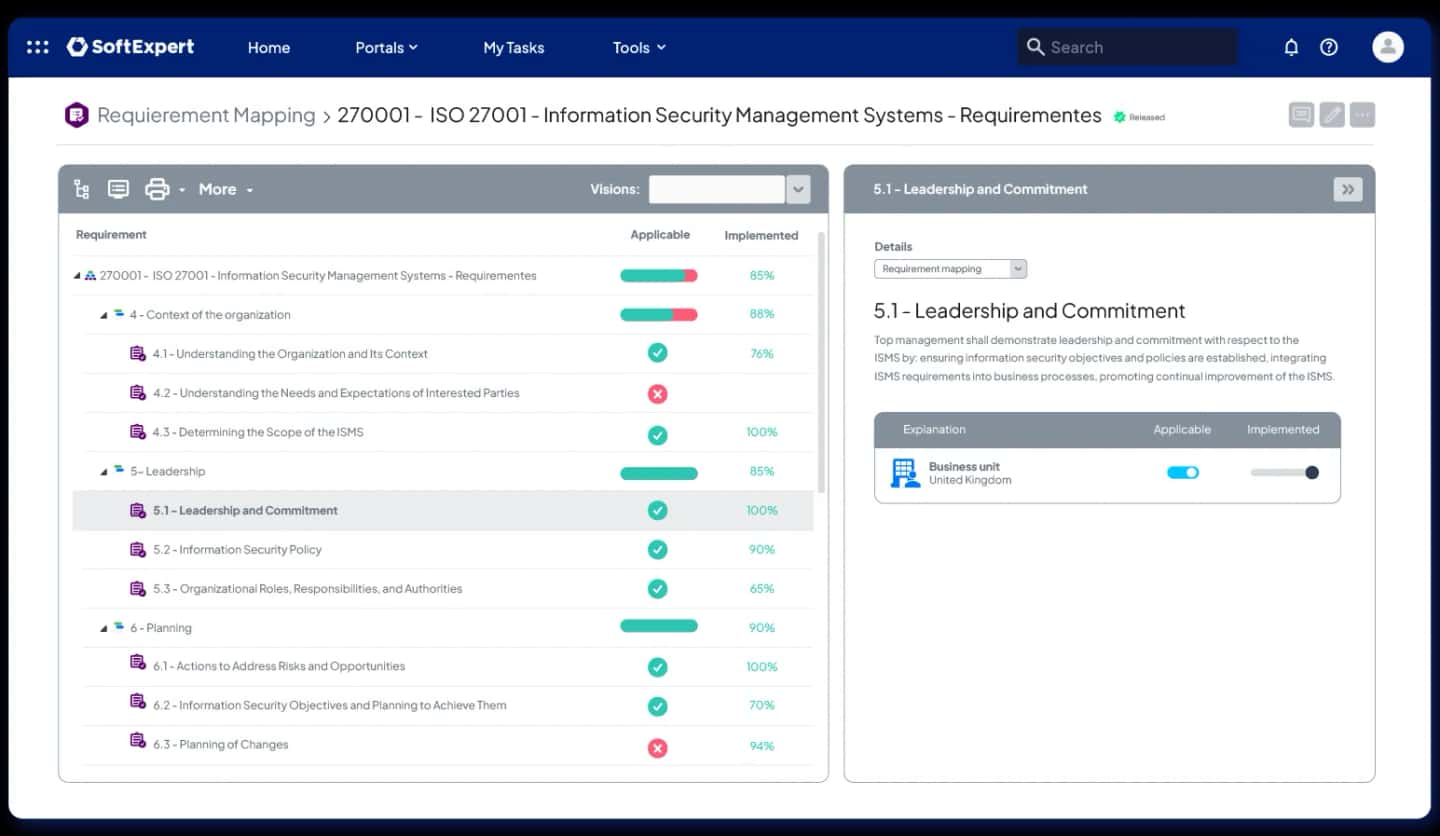
Accelerate your ISO 27001 certification journey
Centralize ISO 27001 requirements and ISO 27001 controls, simplify ISO 27001 audit, and reduce vulnerabilities with ISO 27001 compliance software.
Implement workflows for incident detection and response, strengthening data protection throughout the ISO 27001 certification process.
Improve decision-making with ISO 27001 risk assessment aligned with ISO 27001 certification.
Discover how SoftExpert helps companies achieve compliance with ISO 27001
Anticipate and mitigate risks with agility
Accelerate compliance with the ISO 27001 requirements:
6.1 - Actions to address risks and opportunities
8.2 - Information security risk assessment
8.3 - Information security risk treatment
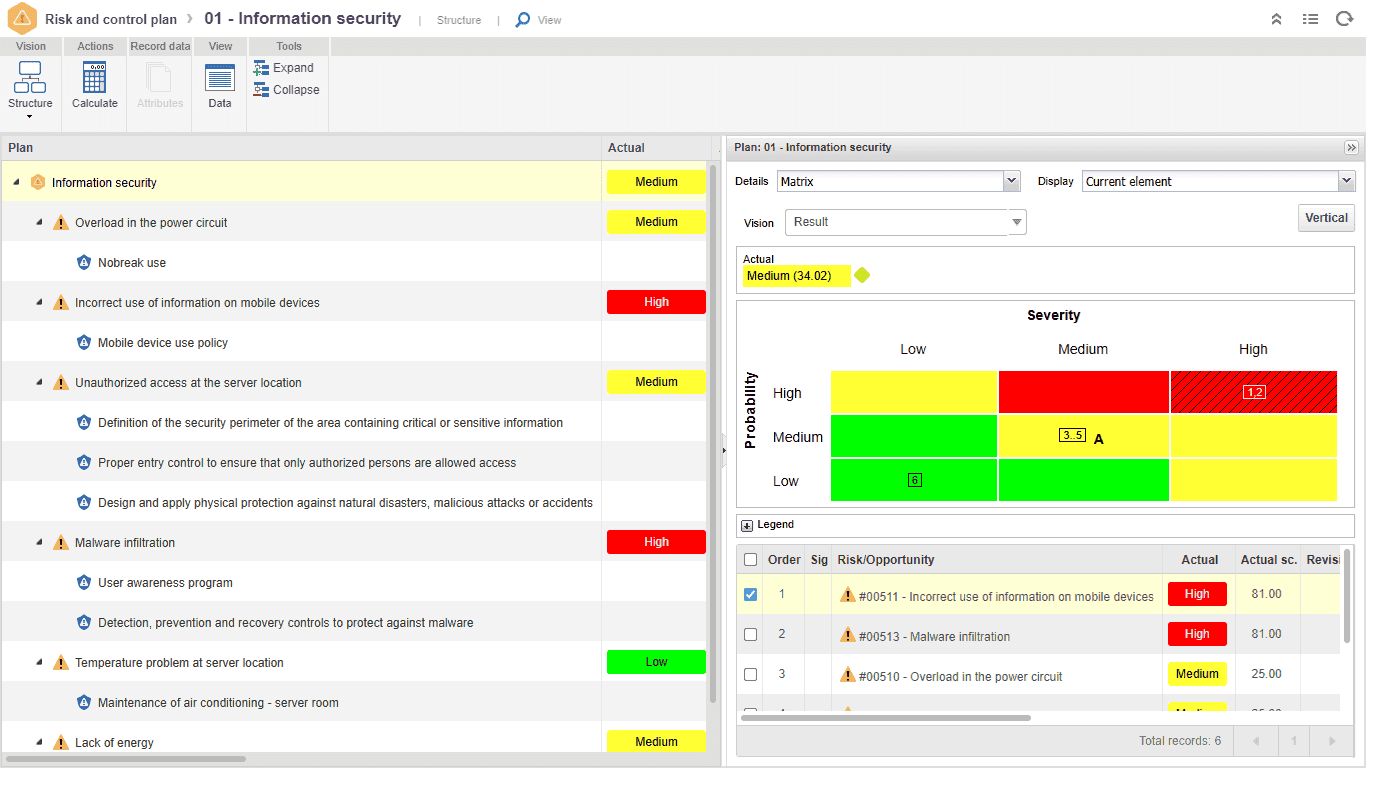
- Identification and management of information security risks
- Centralization and protection of risk information
- Prioritization of preventive actions based on contexts and impacts
- Monitoring of risk and security evolution through intuitive dashboards
Take a tour of the software. Click here →
Simplify your audit management
Accelerate compliance with the ISO 27001 requirement:
9.2 - Internal audit
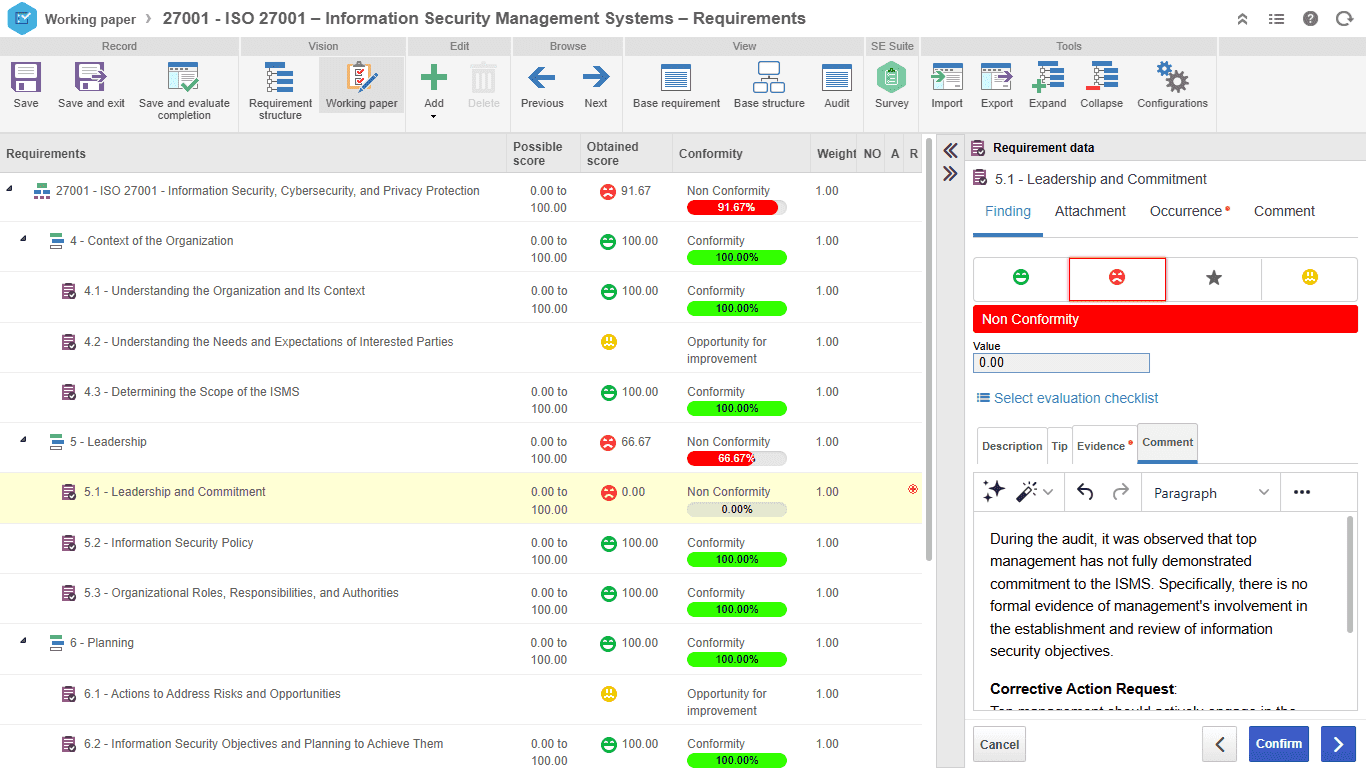
- Creation of audit programs aligned with system needs
- Scheduling and assignment of auditors with defined scopes
- Organized recording and documentation of audit stages
- Compliance assessment at the end of the audit
Take a tour of the software. Click here →
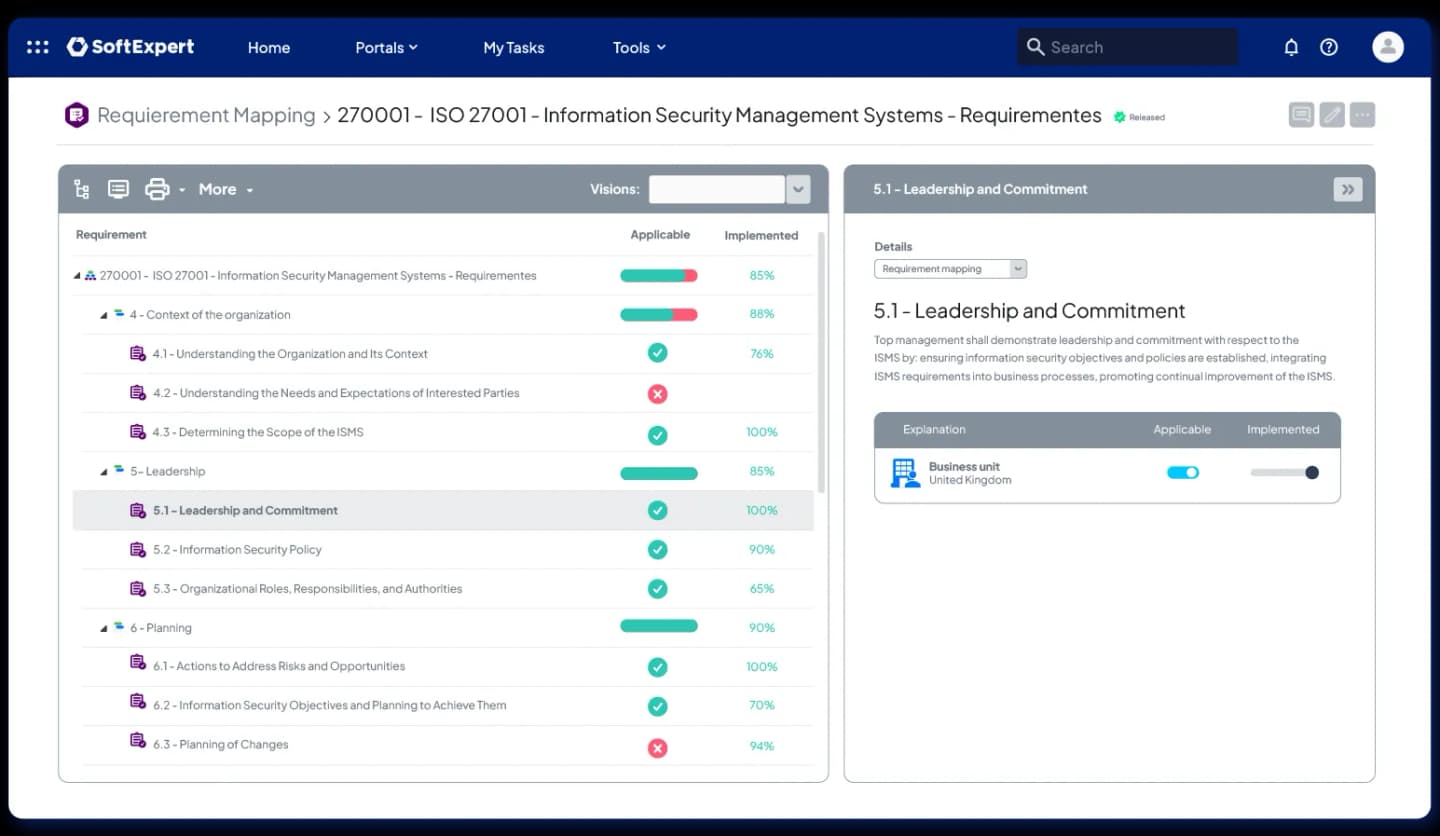
Facilitate audits with the Statement of Applicability
Accelerate compliance with the ISO 27001 requirement:
4.4 - Information security management system
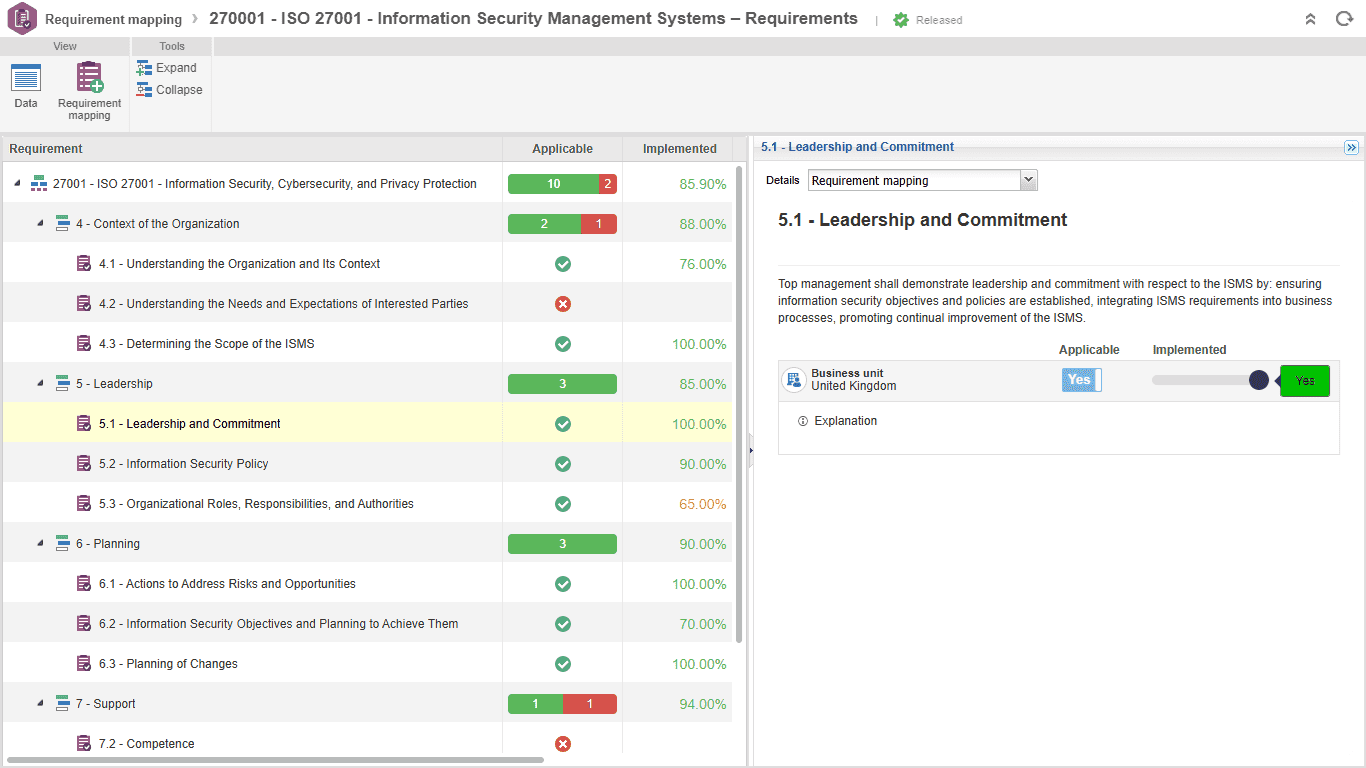
- Structured mapping of requirements and controls
- Associations with documents, processes, and risks
- Planning actions for nonconformity
- Applicability of requirements in the management system
Take a tour of the software. Click here →
Organize and control documents effectively
Accelerate compliance with the ISO 27001 requirements:
7.5 - Documented information
Controls:
A.5.12 - Information classification
A.5.31 - Legal, statutory, regulatory, and contractual requirements
A.5.33 - Protection of records
A.5.36 - Compliance with information security policies, rules, and standards
A.8.3 - Restriction of access to information
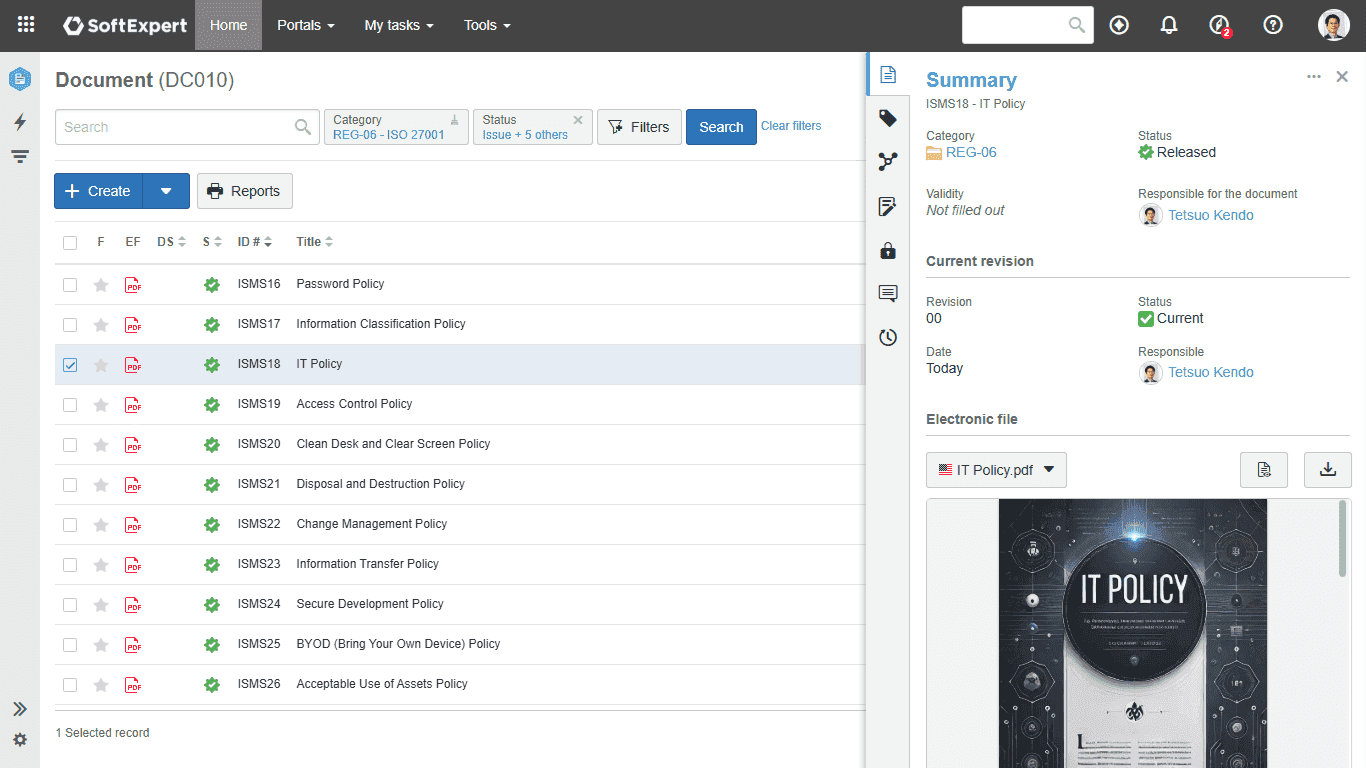
- Automated document version management
- Full traceability of modifications
- Secure access and editing control
- Guaranteed access to valid and secure information
Take a tour of the software. Click here →
Maximize the value and security of your assets
Accelerate compliance with the ISO 27001 requirements:
A.7.8 - Equipment siting and protection
A.7.10 - Storage media
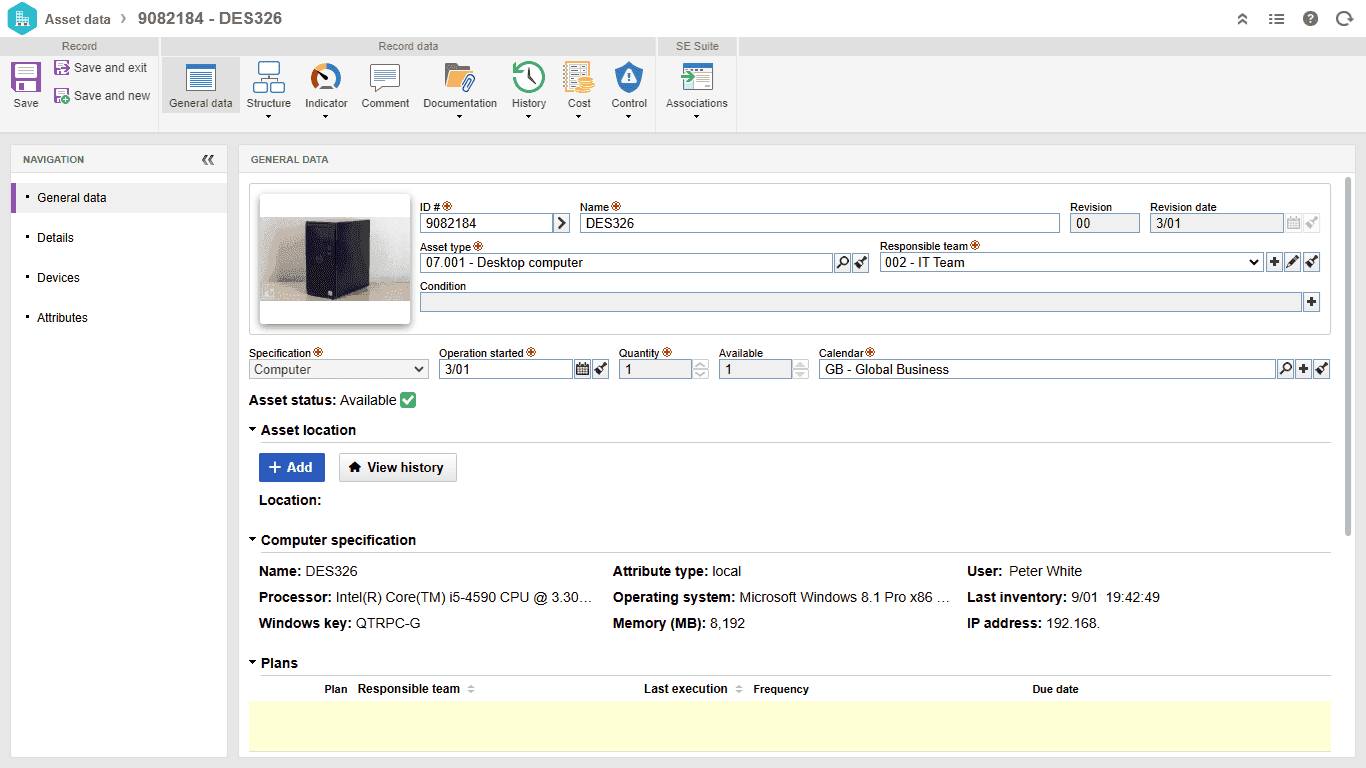
- Efficient asset management throughout the lifecycle
- Centralized and categorized asset inventory
- Tracking of asset movements and changes
- Real-time monitoring of asset status and performance
Take a tour of the software. Click here →
Respond quickly to security incidents
Accelerate compliance with the ISO 27001 requirements:
A.5.24 - Information security incident management planning and preparation
A.5.25 - Assessment and decision on information security events
A.5.26 - Response to information security incidents
A.5.27 - Learning from information security incidents
A.5.28 - Collection of evidence
A.6.8 - Reporting information security events
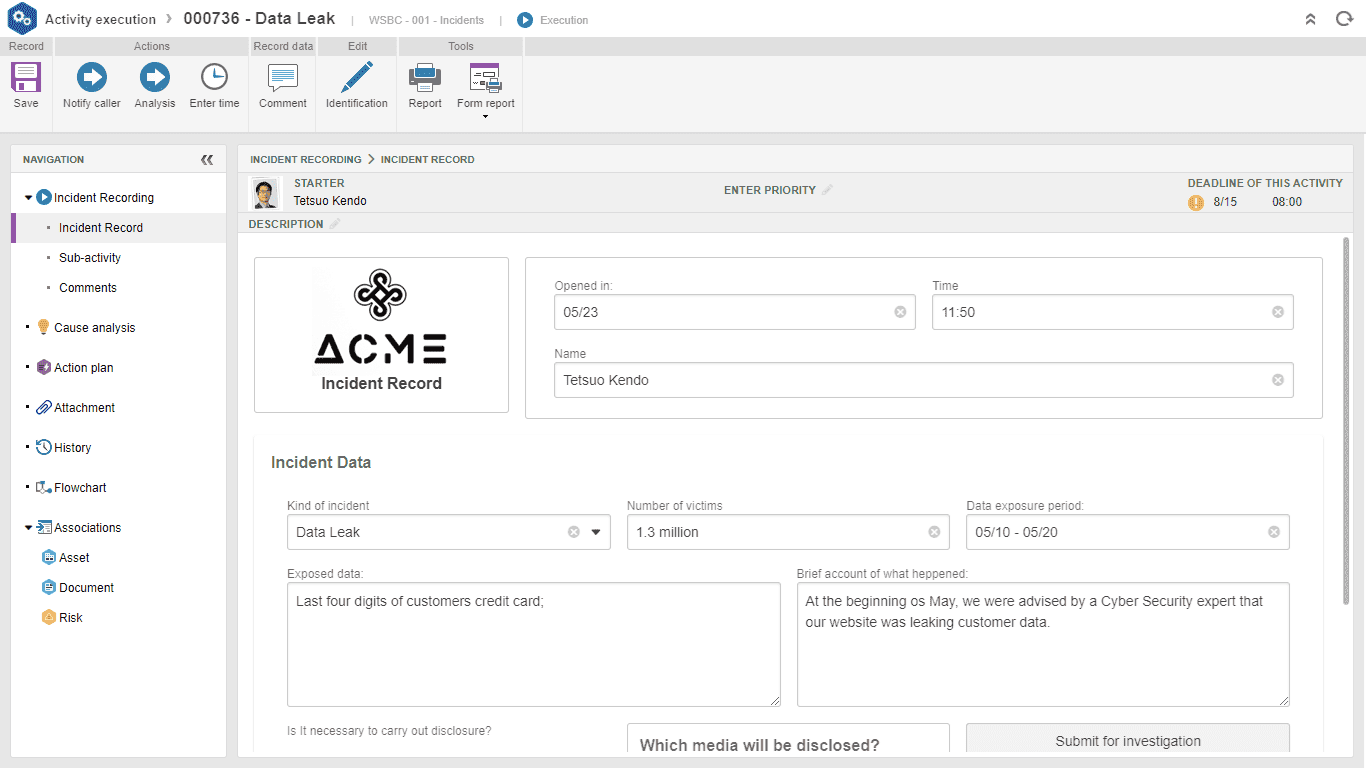
- Agile and standardized registration of security incidents
- Real-time monitoring of incident status and resolution
- Implementation of preventive actions based on lessons learned
Take a tour of the software. Click here →
Evaluate, qualify, and monitor suppliers efficiently
Accelerate compliance with the ISO 27001 requirements:
A.5.19 - Information security in supplier relationships
A.5.22 - Monitoring, review, and change management of supplier services
A.8.30 - Outsourced development
A.8.26 - Application security requirements
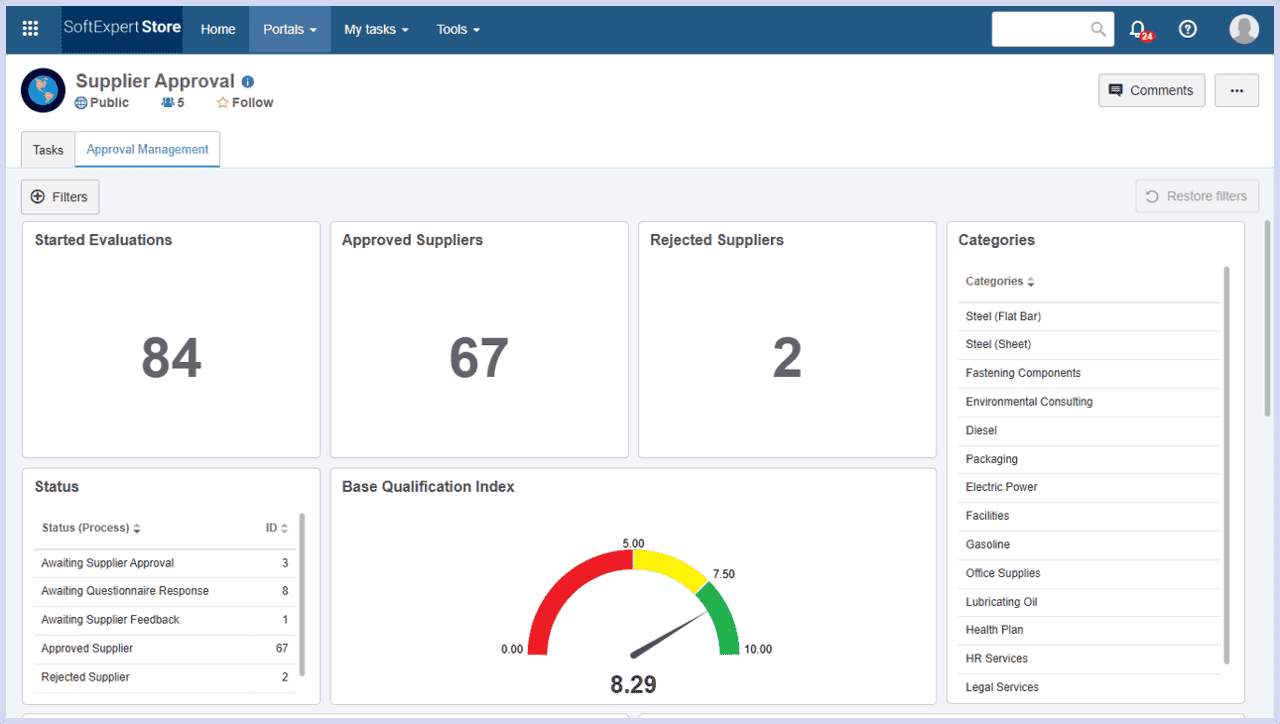
- Evaluation and selection of suppliers with consistent criteria
- Traceability of the supplier approval process
- Standardization of questionnaires and consistency in evaluations
- Generation of performance reports for informed decisions
Take a tour of the software. Click here →
A decision capable of changing the game
Large companies in the market have already recognized our global potential and have become our allies.
Your company could be next.
Glossary
Secure, compliant, and ready to integrate with your ecosystem
Built to connect with your existing stack while keeping governance, traceability, and control at the center.
Frequently Asked Questions
ISO 27001 is an internationally recognized standard that defines the requirements for implementing an Information Security Management System (ISMS). Its main purpose is to help organizations protect sensitive information and manage security risks in a structured and continuous way.
By adopting ISO 27001, organizations can:
- Protect critical data against breaches, unauthorized access, and cyber threats
- Establish structured ISO 27001 controls aligned with business risks
- Implement a continuous ISO 27001 risk management framework
- Ensure compliance with legal, regulatory, and contractual requirements
- Support internal and external ISO 27001 audit processes
- Strengthen governance, trust, and market credibility
With the support of ISO 27001 software, these processes become more automated, traceable, and scalable.
The ISO 27001 certification process follows a structured approach to ensure that an organization’s ISMS meets all ISO 27001 requirements.
This process typically includes:
- Defining the ISMS scope, including assets, systems, and business processes
- Conducting an ISO 27001 gap analysis to identify compliance gaps
- Implementing required ISO 27001 controls and security policies
- Performing a comprehensive ISO 27001 risk assessment
- Preparing and managing required ISO 27001 documentation
- Executing internal audits using an ISO 27001 audit checklist
- Undergoing an external certification audit conducted by an accredited body
Using an ISO 27001 compliance software significantly reduces manual effort and accelerates certification timelines.
ISO 27001 requirements define the essential elements needed to establish, implement, maintain, and continuously improve an ISMS. These requirements include:
- Defining security policies, scope, and governance structure
- Performing continuous ISO 27001 risk assessment and treatment
- Implementing and maintaining ISO 27001 controls
- Managing documentation and evidence (ISO 27001 documentation)
- Assigning roles and responsibilities for information security
- Monitoring performance through audits and reviews
- Driving continuous improvement of the ISMS
Together, these elements ensure a consistent and risk-based approach to information security.
ISO 27001 risk assessment is a core component of the ISMS and ensures that risks are identified, evaluated, and treated effectively. The process involves:
- Identifying information assets and their business value
- Detecting potential threats and vulnerabilities
- Assessing risk impact and likelihood
- Prioritizing risks based on severity
- Selecting appropriate ISO 27001 controls to mitigate risks
- Continuously monitoring and reviewing risks through ISO 27001 risk management
With ISO 27001 software, organizations can automate this process and gain real-time visibility through dashboards and analytics.
ISO 27001 software is a specialized solution designed to support the implementation, management, and maintenance of an ISMS. It helps organizations to:
- Manage and track ISO 27001 requirements and controls
- Automate audit processes and evidence collection (ISO 27001 audit)
- Perform and monitor ISO 27001 risk assessment
- Centralize policies and documentation (ISO 27001 documentation)
- Track progress throughout the ISO 27001 certification process
- Improve traceability, accountability, and efficiency
As a result, organizations can achieve compliance faster and with greater accuracy.
Implementing ISO 27001 provides both strategic and operational advantages, especially for organizations dealing with sensitive data. Key benefits include:
- Reduced security risks through structured ISO 27001 risk management
- Stronger protection of confidential and critical information
- Improved compliance with regulations and industry standards
- Increased trust from customers, partners, and stakeholders
- Better preparedness for ISO 27001 audit processes
- Continuous improvement aligned with ISO 27001 requirements
- Enhanced operational efficiency with the support of ISO 27001 software
These benefits contribute directly to business resilience and competitive advantage.
An award-winning platform recognized by customers
Trusted by users and rated across leading software review platforms for value, usability, and support.
Global Thinking with Local Service
SoftExpert's global presence, with operations on every continent, drives its growth by delivering strong, personalized service tailored to each local market.
Contact us